OpenBao
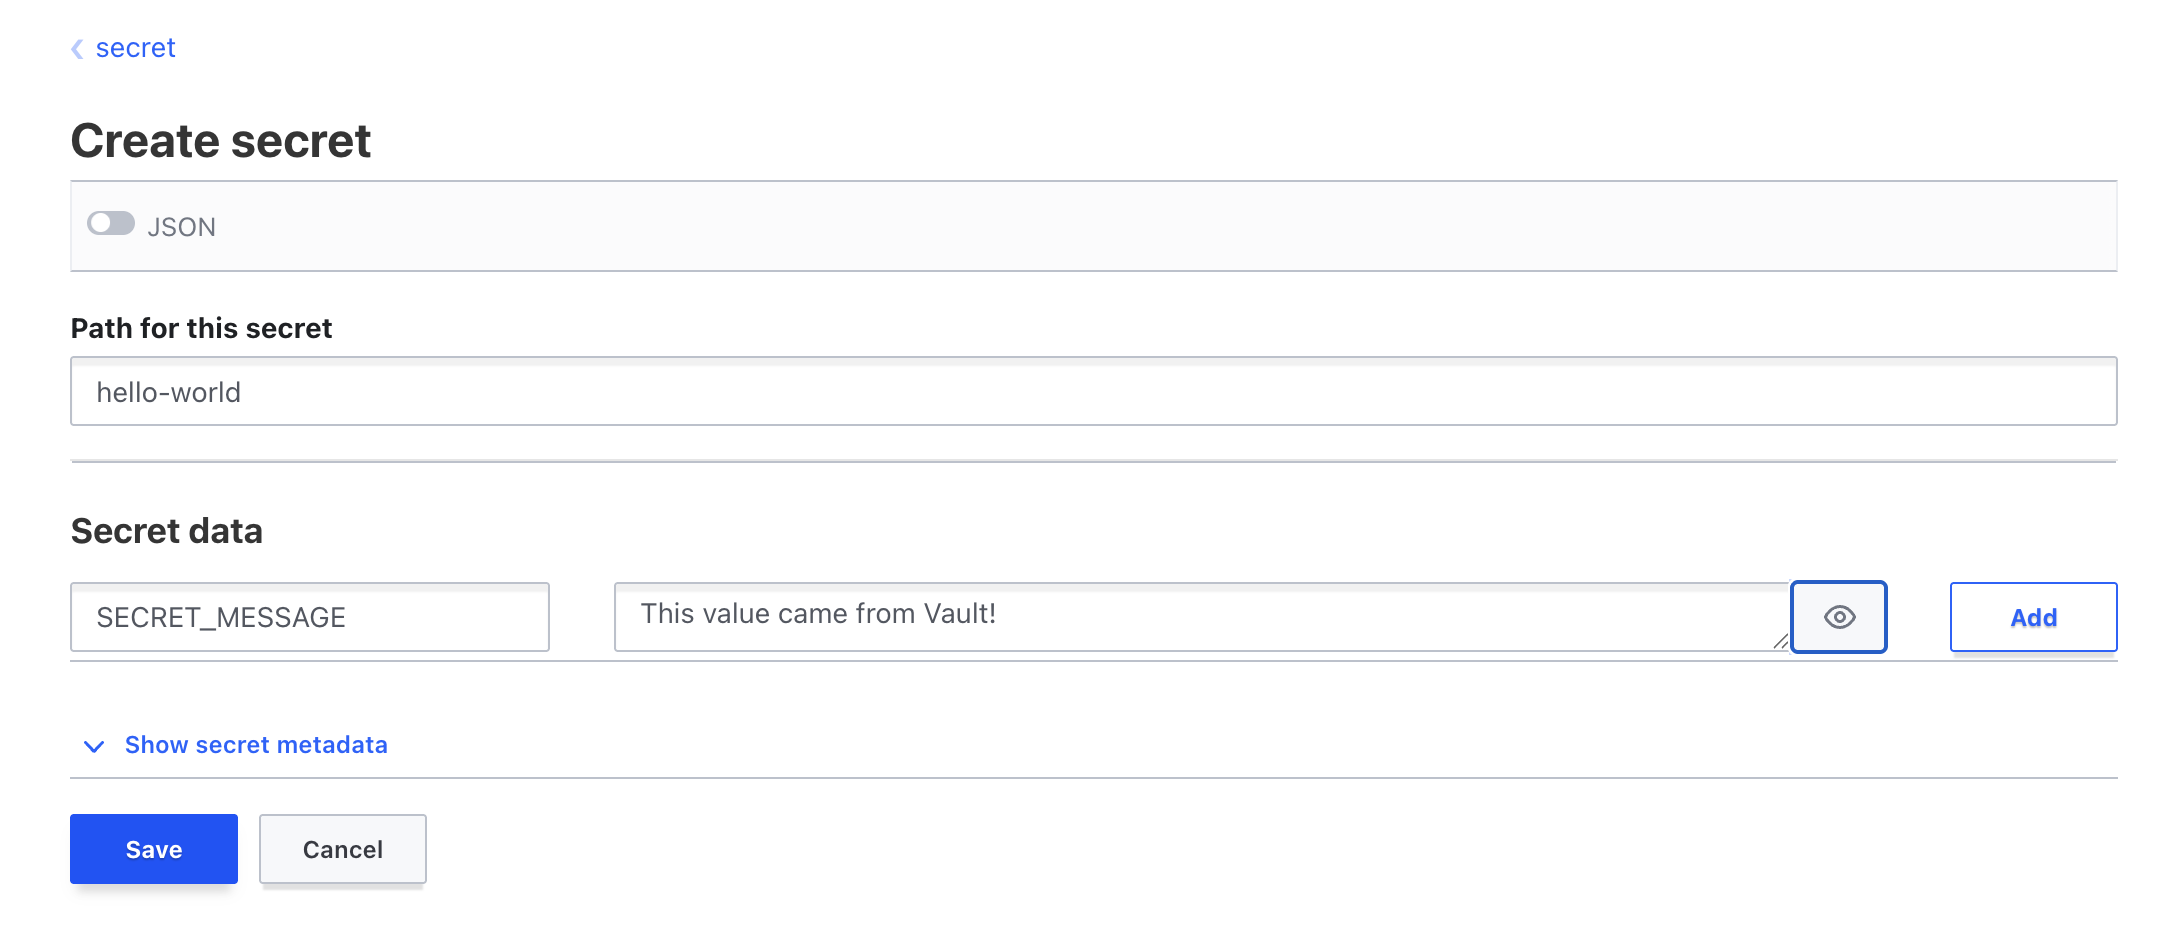
OpenBao is the encrypted secret store in every cluster, running in high-availability mode with its own replicated storage. OpenBao is protected by the platform's single sign-on and is referred to generically as "vault" in the documentation.
 Free assessment
Secrets are kept in an encrypted store inside each cluster and delivered to applications as Kubernetes Secrets. People sign in to the platform's web interfaces with their GitHub accounts.
OpenBao is the encrypted secret store in every cluster, running in high-availability mode with its own replicated storage. OpenBao is protected by the platform's single sign-on and is referred to generically as "vault" in the documentation.
External Secrets Operator copies secrets from OpenBao into Kubernetes Secrets that applications read. The platform connects it to the cluster's OpenBao, so an application only declares which secrets it needs.
Dex is the platform's single sign-on provider. It signs people in with their GitHub accounts, admits only members of the GitHub organizations configured for the cluster, and provides sign-in for Argo CD, Grafana, OpenBao, kubectl and the other platform interfaces.
oauth2-proxy puts the platform's single sign-on in front of web interfaces that have no sign-in of their own, such as the cluster homepage and the load balancer dashboards. Our documentation also shows how to run it in front of your own applications.
GlueOps's own code is released under the Apache License 2.0. Each upstream project keeps its own license, shown in its section. Project names and logos belong to their owners and are shown only to identify each project. Their use does not mean that any project endorses GlueOps.
More of the platform
Questions about the platform?
Book a free assessment and we'll walk through how the platform would run your workloads.
Get a free assessment